The Scramble costs hundreds of hours
Manual evidence collection before every audit burns weeks your team does not have. Comply does it continuously, in the background.

Regulated
Healthcare & DentalFinancial ServicesLaw FirmsAccounting & Tax FirmsGovernment & Defense ContractorsAI & Technology CompaniesArchitecture, Engineering & ConstructionEveryone else
Retail & Multi-Location StoresManufacturing & Machine ShopsReal Estate Brokerages & TitleNonprofits & AssociationsAuto Repair & Skilled TradesRestaurants, Hotels & HospitalityPrivate Schools & TutoringAgencies, Staffing & ConsultanciesThe annual audit scramble is dead. AccuSights Comply benchmarks your business against multiple frameworks, drafts your policies, and collects evidence automatically all year. You stay audit-ready every day, while your team gets its hundreds of lost hours back.
One vault, every framework, always current. This is what audit-ready looks like all year.
Illustrative view. Your real scores come from your own environment.
Most businesses ignore security for 11 months, then panic for 30 days before the auditor shows up. That is compliance theater. Threats do not wait for your Q4 schedule, and a certificate from last March does not protect you today.
A point-in-time audit is a photo. The moment it is taken, it is out of date. Continuous compliance is a live feed.
The old way, and most checklists
Audit-ready every single day
We guide you from selection through certification readiness, then keep you there with continuous monitoring.
Choose from multiple pre-built frameworks, or build a custom standard. We tell you which ones your business and industry actually require.
Our engine benchmarks your environment against your targets, finds exactly where the gaps are, and recommends the evidence and fixes you need.
Get tailored policies written for your business and a prioritized remediation roadmap, not generic templates you have to rewrite.
Comply connects read-only to your systems, verifies controls, and collects evidence automatically. Cross-mapped across every framework at once.
Stay audit-ready year-round. We track regulatory changes and flag drift the moment a control slips, so there is never another scramble.
Automates control monitoring and evidence collection across multiple frameworks at once, cutting redundant work and cost.
Tailored policies generated for your business and aligned to NIST, CIS, ISO, and your other target standards.
Centralized, always-current evidence. Connects in read-only mode, so there is nothing to install and no risky access.
One piece of evidence satisfies many controls. Pursue several certifications without doing the work several times.
Real-time control validation that catches a broken control the day it breaks, not at next year's audit.
We watch the standards so you do not have to, and update your program when the rules move.
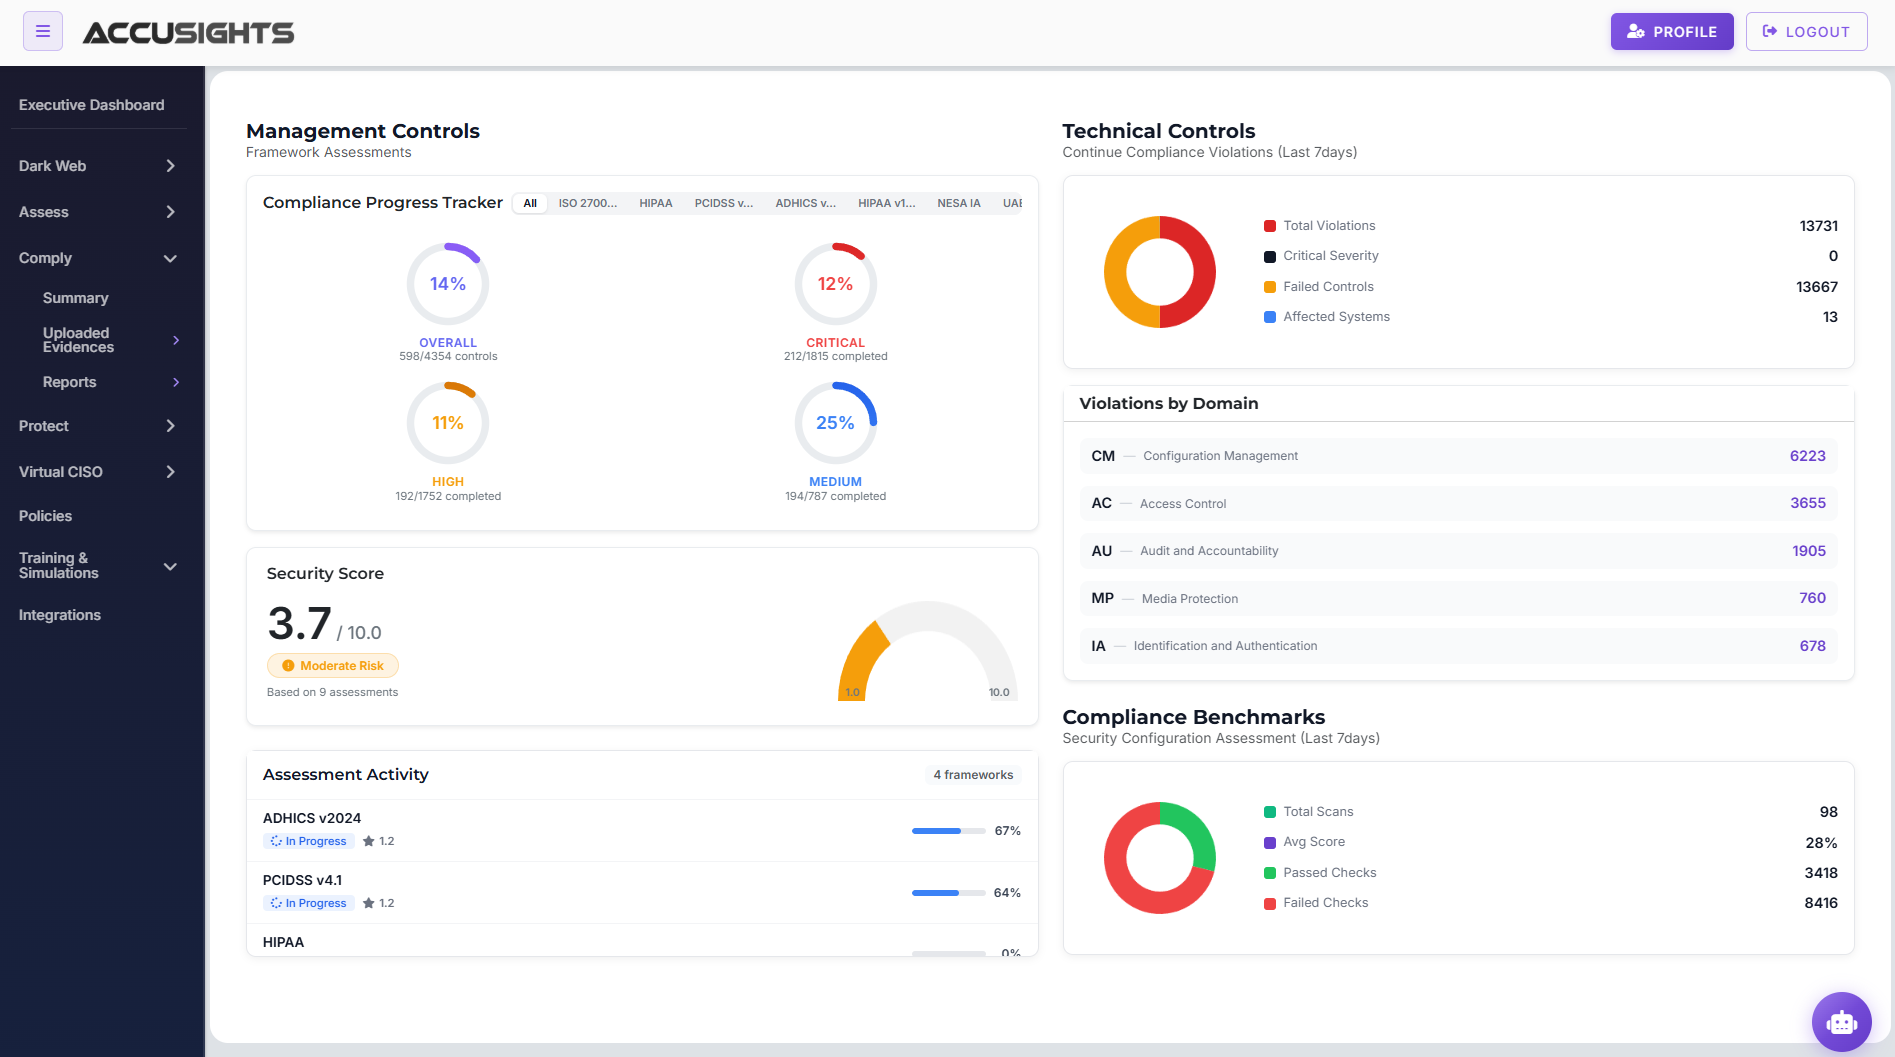
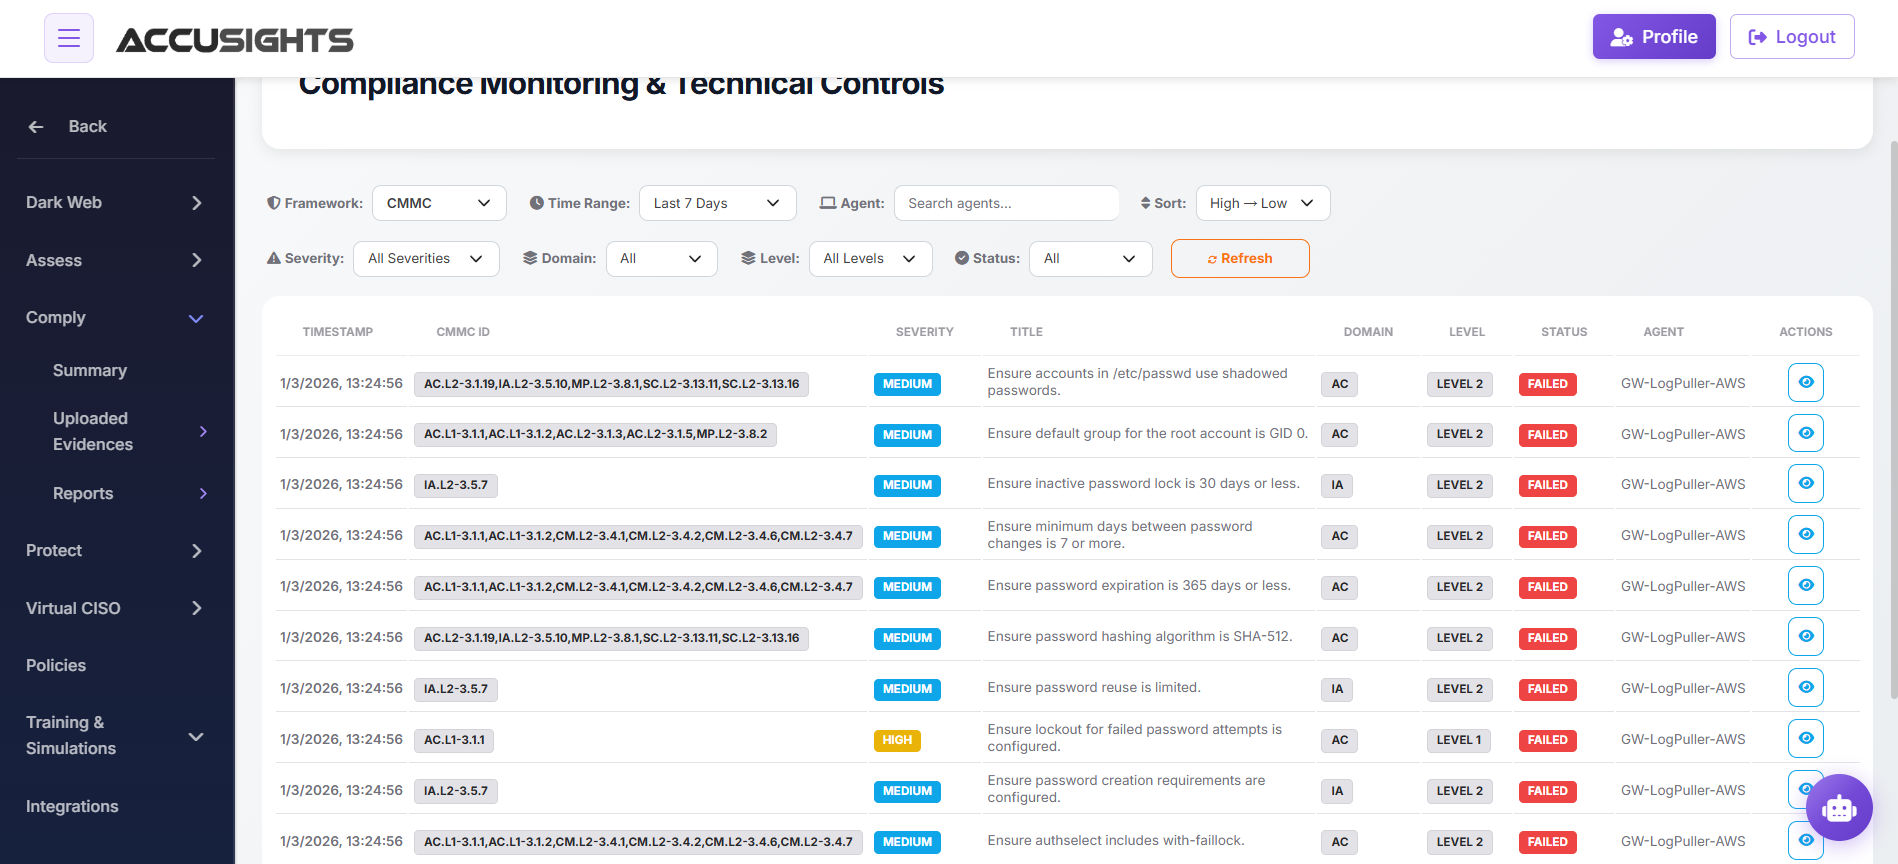
No spreadsheets, no shared drives full of stale screenshots. Your whole compliance posture lives in one place, updated automatically, so you always know exactly where you stand and what is left to do.
One score for each standard, always current.
Drill into any control to see its evidence and status.
Hand an auditor a clean, current package in minutes.
Vanta, Drata, and Secureframe treat the certificate as the goal. We treat it as the byproduct of being genuinely secure, because a badge on a wide-open business is just a target with paperwork.
Vanta, Drata, Secureframe
Compliance on top of real security
Start by finding the gaps, then keep them closed and watched. One partner, one dashboard.
Assess shows you exactly where you stand across every major framework, with a ranked fix plan. It is the fastest way to begin a compliance program.
Explore AssessThe 24/7 managed AI SOC enforces the controls compliance requires, monitoring your email, devices, and cloud and shutting down threats in seconds. Priced per employee.
Explore ProtectGet a clear read on your compliance posture across HIPAA, CMMC, SOC 2, and PCI, and a prioritized roadmap to close the gaps.
Talk it through with a compliance specialist.
We focus on the frameworks your industry and contracts actually require.
What to fix first to get certification-ready fastest.
Twelve questions, about three minutes. You get a score, the gaps behind it and the fixes that move it most. No sales gate, no card.
Prefer to talk? Call +1 (773) 747-7490.