The Scramble costs hundreds of hours
Manual evidence collection before every audit burns weeks your team does not have. Comply does it continuously, in the background.

Regulated
Healthcare & DentalFinancial ServicesLaw FirmsAccounting & Tax FirmsGovernment & Defense ContractorsAI & Technology CompaniesArchitecture, Engineering & ConstructionEveryone else
Retail & Multi-Location StoresManufacturing & Machine ShopsReal Estate Brokerages & TitleNonprofits & AssociationsAuto Repair & Skilled TradesRestaurants, Hotels & HospitalityPrivate Schools & TutoringAgencies, Staffing & ConsultanciesAccuSights Comply benchmarks your business against multiple frameworks, drafts your policies, and collects evidence automatically all year. Evidence stays current every day with continuous monitoring, while your team gets its hundreds of lost hours back.
One vault, every framework, always current. This is what audit-ready looks like all year.
Illustrative view. Your real scores come from your own environment.
Most businesses ignore security for 11 months, then rush for 30 days before the auditor shows up. Threats do not wait for your Q4 schedule, and a certificate from last March does not protect you today.
A point-in-time audit is a photo: out of date the moment it is taken. Comply checks the same controls on a schedule, all year.
The old way, and most checklists
Audit-ready every single day
We guide you from selection to assessment readiness, then keep you there with continuous monitoring.
A note on authority: the regulator, auditor or certifying body has the final say on whether you comply. We help interpret the requirements, scope what applies, gap-assess against what is published today, and keep you compliance-ready and secure as the guidance evolves. We hold no regulatory authority and do not certify.
Choose from multiple pre-built frameworks, or build a custom standard. We tell you which ones your business and industry actually require.
Our engine benchmarks your environment against your targets, finds exactly where the gaps are, and recommends the evidence and fixes you need.
Get tailored policies written for your business and a prioritized remediation roadmap, not generic templates you have to rewrite.
Comply connects read-only to your systems, verifies controls, and collects evidence automatically. Cross-mapped across every framework at once.
Readiness maintained year-round. We track regulatory changes and flag drift when a control slips, so the pre-audit scramble goes away.
Automates control monitoring and evidence collection across multiple frameworks at once, cutting redundant work and cost.
Tailored policies generated for your business and aligned to NIST, CIS, ISO, and your other target standards.
Centralized, always-current evidence. Connects in read-only mode, so there is nothing to install and no risky access.
One piece of evidence satisfies many controls. Pursue several certifications without doing the work several times.
Real-time control validation that flags a broken control on the next scheduled check, typically the same day, not at next year's audit.
We watch the standards so you do not have to, and update your program when the rules move.
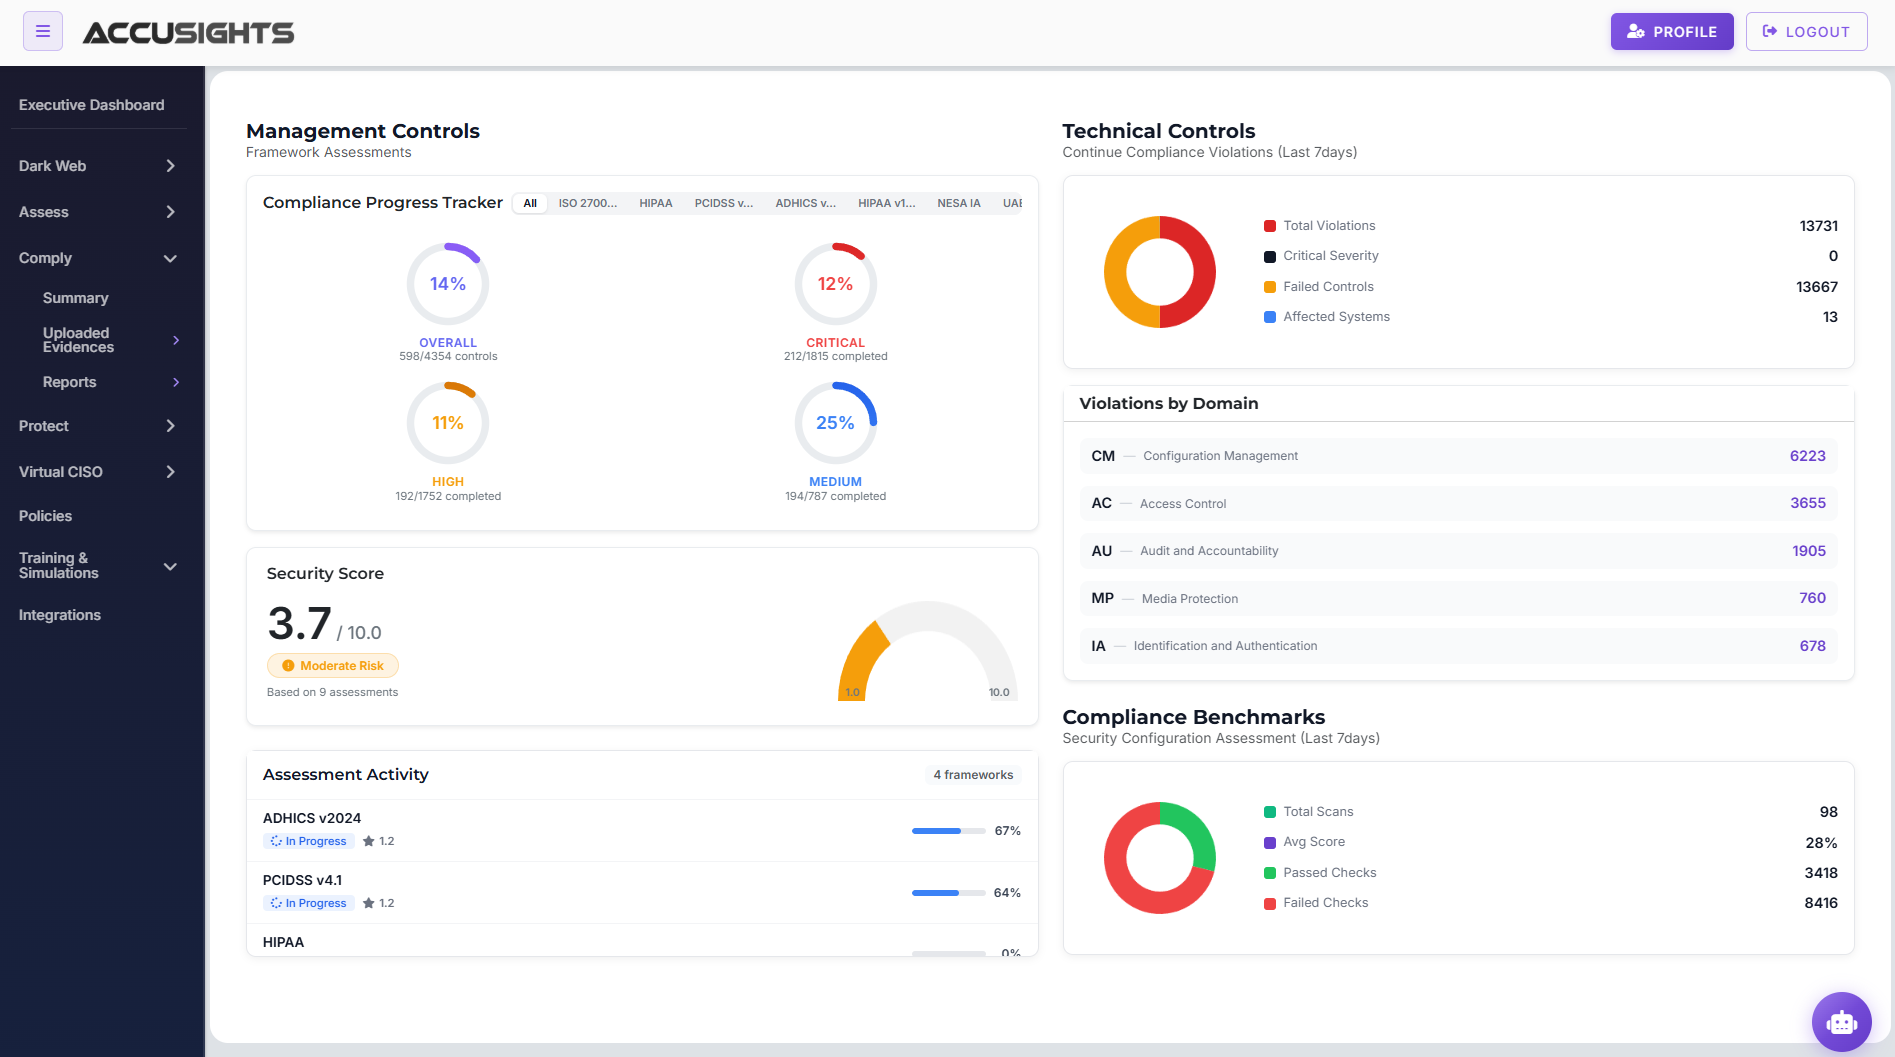
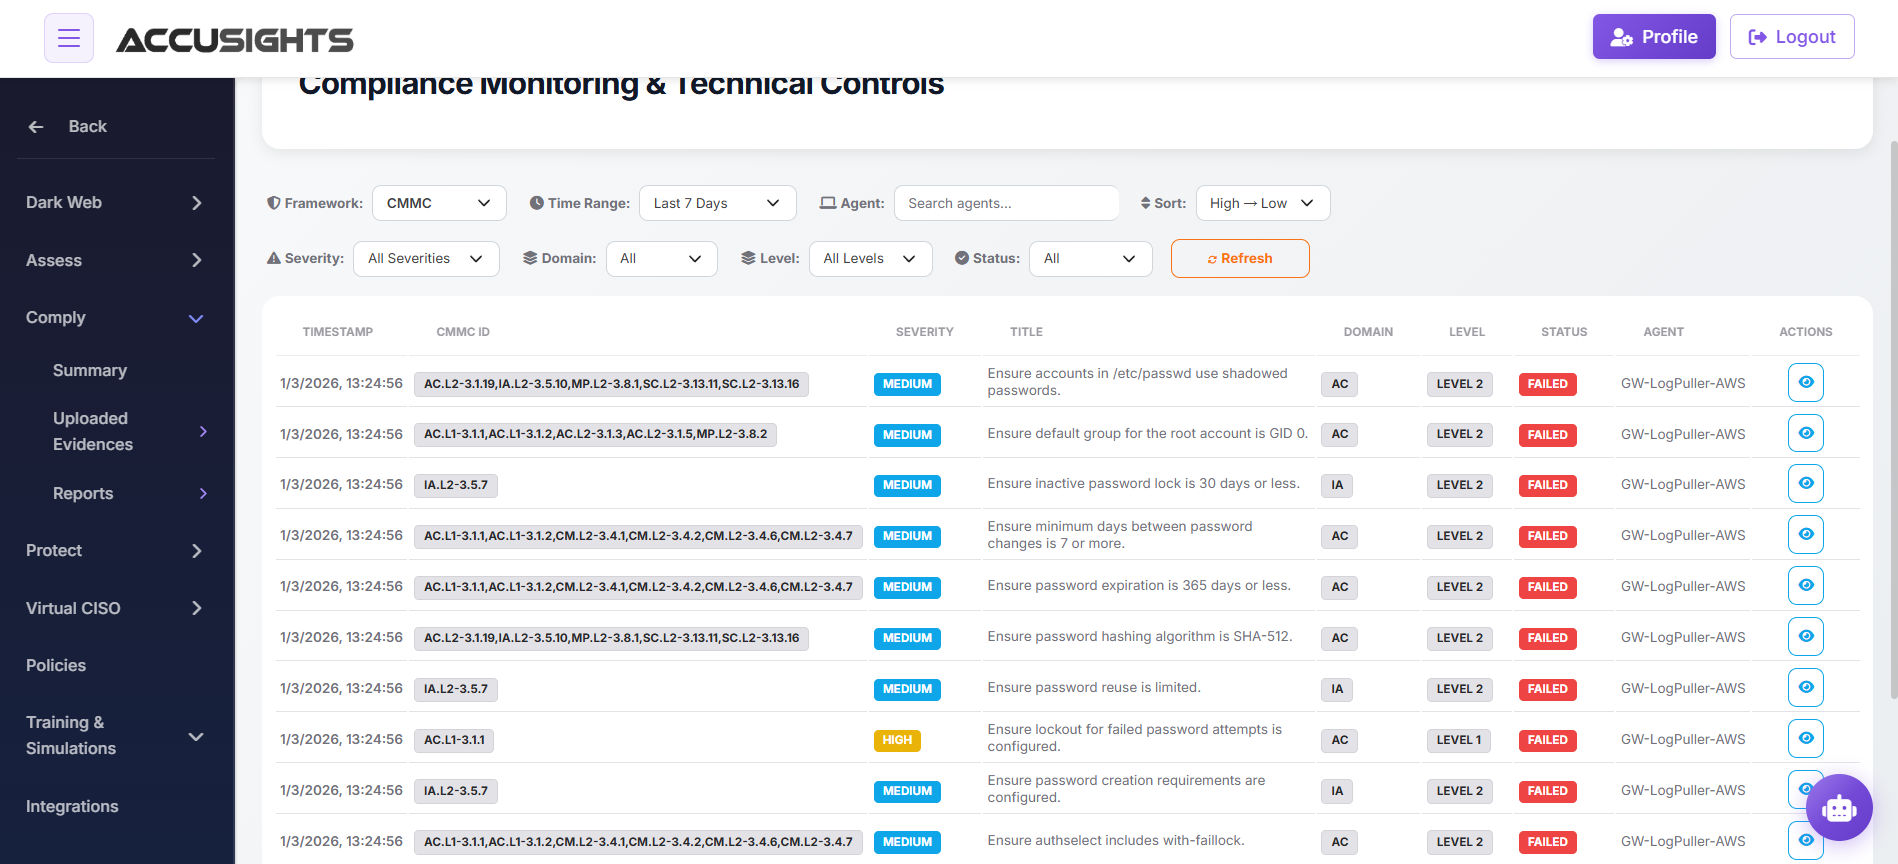
No spreadsheets, no shared drives full of stale screenshots. Your whole compliance posture lives in one place, updated automatically, so you always know exactly where you stand and what is left to do.
One score for each standard, always current.
Drill into any control to see its evidence and status.
Hand an auditor a clean, current package in minutes.
Some compliance-automation platforms treat the certificate as the product and leave security as your problem. We treat it as the byproduct of being secure: the controls that pass the audit are the ones that stop the attack.
Compliance-automation platforms
Compliance on top of real security
Start by finding the gaps, then keep them closed and watched. One partner, one dashboard.
Assess shows you exactly where you stand across every major framework, with a ranked fix plan. It is the fastest way to begin a compliance program.
Explore AssessProtect enforces the controls compliance requires: AI monitoring of your computers and email day and night, sign-ins and cloud accounts added at onboarding, threats contained in seconds in typical cases, and an engineer who calls you on any critical finding (times are typical, not a promise). Priced per employee.
Explore ProtectTraditional compliance is a snapshot. You scramble for 30 days, pass the audit, then ignore it for 11 months while threats keep coming. Continuous compliance flips that. AccuSights Comply monitors your controls year-round, collects evidence automatically, and keeps your evidence current every day, so compliance is something you have, not something you cram for.
CMMC 2.0, HIPAA, SOC 2, ISO 27001, PCI DSS, NIST CSF, CIS Controls, GDPR, EU NIS2 and FINRA, plus the rest of our 18-framework catalogue, including NIST SP 800-171, NYDFS Part 500 and the FTC Safeguards Rule. Our engine cross-maps evidence across frameworks, so work you do for one counts toward the others.
Not necessarily. Comply connects in read-only mode to your evidence sources and verifies controls automatically, with no write access. An agent is optional: it collects evidence from devices and servers that have no other source.
Some compliance-automation platforms treat the badge as the goal. We treat compliance as a byproduct of being secure. Comply automates the evidence and policies, but it sits on top of real security work from Assess and Protect, so your attestation reflects an actual locked door, not just paperwork.
Yes. The AI engine benchmarks your environment against your target frameworks, identifies exactly where the gaps are, and generates tailored policies that move you toward certification readiness. You get policies written for your business, not generic templates you have to rewrite.
No. AccuSights is not a C3PAO and does not certify anyone. We get you ready: scoping, the gap assessment, your SSP and POA&M, an honest SPRS score and the fixes. Third-party Level 2 assessments were paused in July 2026, but DFARS 7012, NIST SP 800-171 and SPRS still apply. Paused, not gone.Source: DefenseScoop, 13 July 2026
Not from the government. HHS says covered entities are not required to certify compliance with the Security Rule and does not endorse any certification. What regulators ask for is evidence: a current risk analysis, policies people follow and safeguards that work. That is what we help you build.Source: HHS Security Rule FAQ
Four things: what you have (devices, accounts, cloud apps, data), how it is protected, where the gaps are, and what to fix first. You get a written report in plain words, a ranked roadmap with a cost and an owner for each fix, and the frameworks that apply to you. Not a scanner printout.
Yes. We assess against one control set, built on CIS Controls v8.1, and map it to each framework that applies to you: HIPAA, CMMC, SOC 2, PCI DSS or others. One piece of evidence then answers several auditors, which keeps the work and the cost down.
Each control is checked against your environment on a schedule, drift raises a ticket before it becomes an audit exception, and the evidence for every framework comes from the same checks. We re-assess on a set rhythm, so the roadmap stays true between audits and not just on audit day.
No. Many clients have a trusted IT provider or managed service provider, and they do the work. We write the plan so they can follow it, answer their questions, and verify each fix in your real setup. If you have no provider, or yours is stretched, we do it ourselves.
Get a clear read on your compliance posture across HIPAA, CMMC, SOC 2, and PCI, and a prioritized roadmap to close the gaps.
Talk it through with a compliance specialist.
We focus on the frameworks your industry and contracts actually require.
What to fix first to get certification-ready fastest.
Twelve questions, about three minutes. You get a score, the gaps behind it and the fixes that move it most. No sales gate, no card.
Prefer to talk? Call +1 (773) 747-7490.