
Cybersecurity, compliance and GRC · For small and mid-size businesses
Real security for your business. Not just a compliance badge.
Most security software helps you pass an audit. We keep you from getting breached. AccuSights finds your gaps, gets you compliant across every framework that applies, and puts AI-powered, human-enabled security on your business. For owners and compliance teams, with or without an IT department.
Public pricing · Named engineer, not a ticket queue · SOC-grade protection at a small-business price
Protect · AI-powered, human-enabled
Take the vacation. We keep the watch.
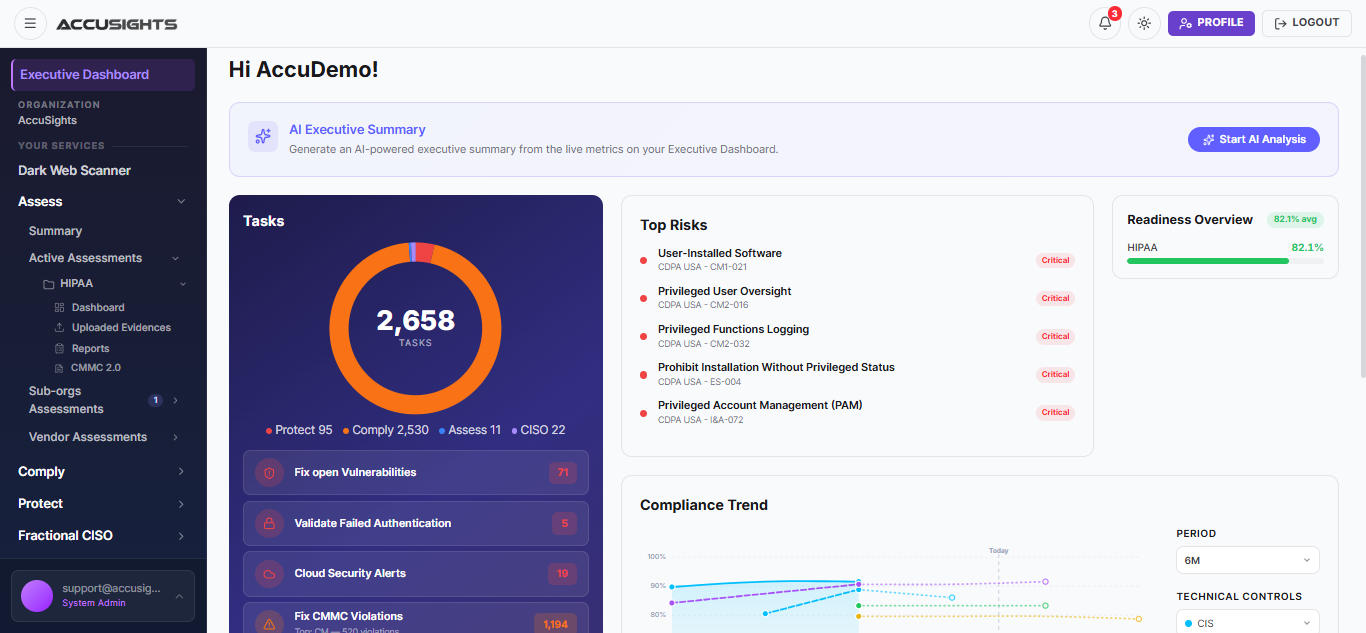
Protect is AI-powered and human-enabled: Aegis, your AI security agent, watches your computers and your email (Microsoft 365 or Google Workspace) day and night and shuts threats down in seconds, and a named Cyber Success Engineer who knows your company calls you on any critical finding. Sign-ins and cloud accounts are added during onboarding as your setup allows.
- A named engineer who knows your environment, not a ticket queue
- AI response in seconds around the clock; engineers on duty 5 days a week, 10 hours a day, and for emergencies any time
- Computers and email from day one, dark-web watch included, the rest added as your setup allows
- One flat, published price per employee. From $25 per user per month
The overnight report above is what waking up looks like with Protect: handled, documented and summarized over your coffee.
How it works
Three steps. One platform. One team behind it.
Start anywhere. Most owners begin with the 3-minute test, fix what matters, then hand us the watch.
Find the gaps before an attacker does.
A clear, honest read on your posture: the 3-minute test today, the full assessment in one to three weeks. Every endpoint, server and cloud inventoried, controls tested, and every gap ranked by what would actually hurt.
Audit-ready across every framework, all year.
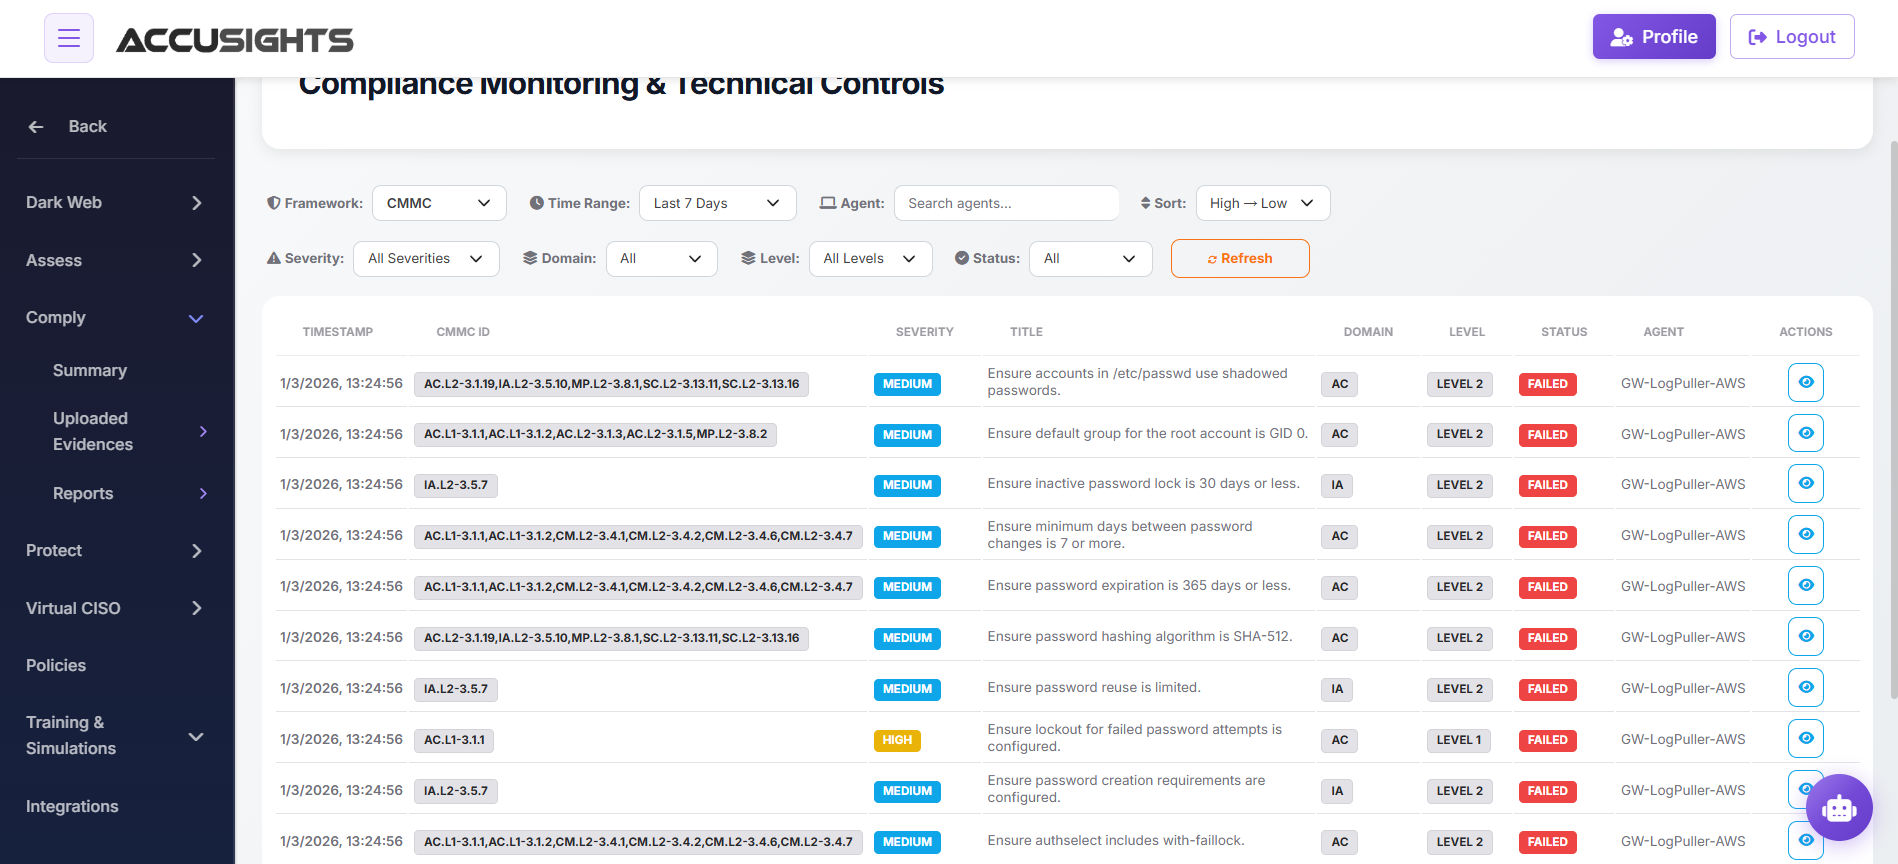
The annual scramble is dead. Evidence collects itself, policies are drafted for you and controls are watched continuously, so the evidence is ready whenever an auditor asks.
Hand us the watch and keep it for good.
The overnight report above becomes your normal. Aegis watches your computers and email day and night and shuts threats down in seconds, and your named engineer calls you on any critical finding, at your desk or on a beach.
Get compliant · One control set, every framework
The three that win deals and keep licenses. Then everything else, from the same work.
The report that wins contracts.
Type I in weeks to unblock the deal, Type II without a year of screenshots. One report answers the 300-question vendor form every time it lands, and the same evidence carries to ISO 27001 when the next buyer asks.
Healthcare runs on trust. We keep yours provable.
A risk analysis that holds up in front of OCR, safeguards implemented rather than promised, staff trained, and patient records watched every day, so a regulator’s letter from evidence you already keep.
A pause is not a pardon.
DoD paused the Phase 2 mandate on July 13, 2026 and took the C3PAO requirement out of contracts on September 3; DFARS 7012, SPRS scores and the 72-hour incident clock did not move. Gap readiness to 110, an SSP and POA&M a C3PAO expects, and a CUI enclave that shrinks the scope, from $6,000.
SOC 2HIPAACMMC 2.0PCI DSSCIS ControlsGDPREU NIS2FINRANot sure which you need? Two minutes →
Healthcare practices in major cities: an engineer comes on site and sets up the critical controls the same week.
Built for your world
Your industry has its own threats. And its own page.
Our stance
The compliance tools sell you a badge. We sell you protection.
The badge platforms are built to help a startup CTO pass an audit. That is paperwork, and paperwork does not stop a breach. AccuSights is security first; then the same work makes compliance the easy part.
The compliance-badge tools
Sell you a certificate to close a deal, while the back door stays open between audits.
Built for a startup CTO or a GRC team you do not have, driving a self-serve portal alone.
Pricing hidden behind a sales demo, and nobody watching at 2am.
AccuSights: security first
Protect the business every day, then use the same work to pass every audit that comes.
A dedicated engineer plus an AI agent that does the work, in plain English, for the owner.
Pricing published right here, a 3-minute Cyber Hygiene Test, and Protect: AI watching day and night, with an engineer who calls you on any critical finding.
You should not need a full-time CISO to be secure. You need the right controls, run every day, and that is the work we do.
Never too big or too small. Let's talk about your cyber anxieties.
Thirty minutes with an engineer, not a salesperson: where you stand, what would change first, and what it costs, with the price on the page. Or start with the 3-minute test and see your score immediately.